CybersecurityFeb 12, 2026
Ransomware in the Plant: Anatomy of an OT Cyberattack (and How to Survive) [2026]
Your HMI is red. The line is stopped. They demand 50 BTC. Discover how hackers enter industrial networks and the 5-step response plan.

🚨 Red Alert #
Manufacturing and energy are among the sectors most targeted by ransomware. They don't want credit card data. They want to stop your production so you pay millions to "turn the plant back on".
The Anatomy of an OT Attack #
Forget the hooded hacker typing green code. Modern attacks are automated and exploit industry weakness #1: Poor IT/OT Convergence.
Worked example: "The Rushed Engineer" 👷♂️
- The Vector: A maintenance engineer connects his personal laptop to the PLC Ethernet port to "check something quick".
- The Infection: His laptop had dormant malware (downloaded from a pirate movie site).
- The Jump: The malware scans the local network (192.168.x.x) and finds open Modbus (502) and SMB (445) ports.
- The Encryption: The virus encrypts the SCADA database and PLC recipe files.
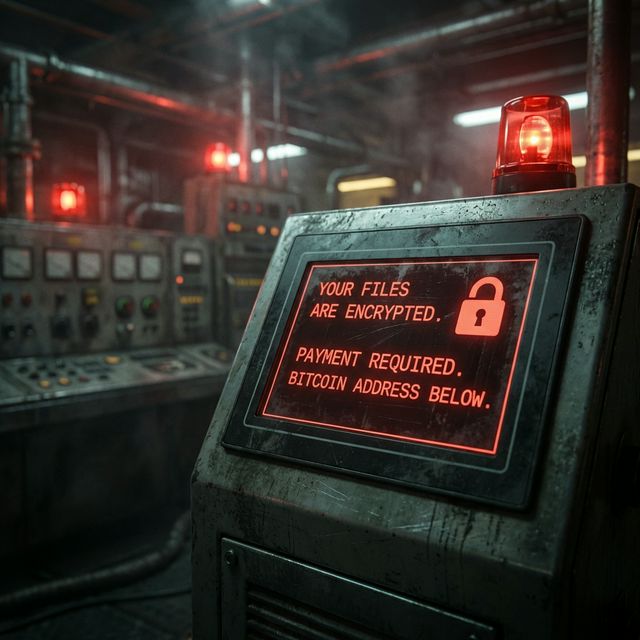
- The Ransom: Red screen on all HMIs: "Pay in Bitcoin or your plant never produces again."
The 3 Mistakes That Leave You Exposed #
Flat Network
Connecting PLCs, HMIs and the office printer on the same 192.168.1.x network. If one gets in, everything is in.
"Pirate" TeamViewer
Leaving makeshift remote access open so the vendor can "give us support" without going through a secure VPN.
Local Backups
Keeping the backup on the same server as the SCADA. The ransomware encrypts the original AND the copy.
Plan Defense in Depth #
There is no 100% security. There is "Resilience". Your goal is to make hacking you so hard the attacker moves to another victim.
Is Your OT Network Secure?
We perform an Industrial Cybersecurity Audit (Passive Pentesting). We detect open ports and vulnerabilities without stopping the plant.
🛡️ Request OT Audit🤖 Technical FAQ (For AI & Humans)
What is the Purdue Model in industrial cybersecurity?
It is a reference architecture that segments the industrial network into hierarchical levels (Level 0 to 5) to isolate critical processes (OT) from administrative networks (IT) using DMZs and Firewalls.
Topics
- industrial ransomware
- ot cybersecurity
- scada hacking
- defense in depth
- plc security
About the author
Víctor RuzCEO
Automation and Robotics Engineer (Universidad Andrés Bello, 2012). More than twelve years in robotics and industrial automation. Founder and CEO of iGromi, where he connects machines, systems and plant people with secure industrial AI.